
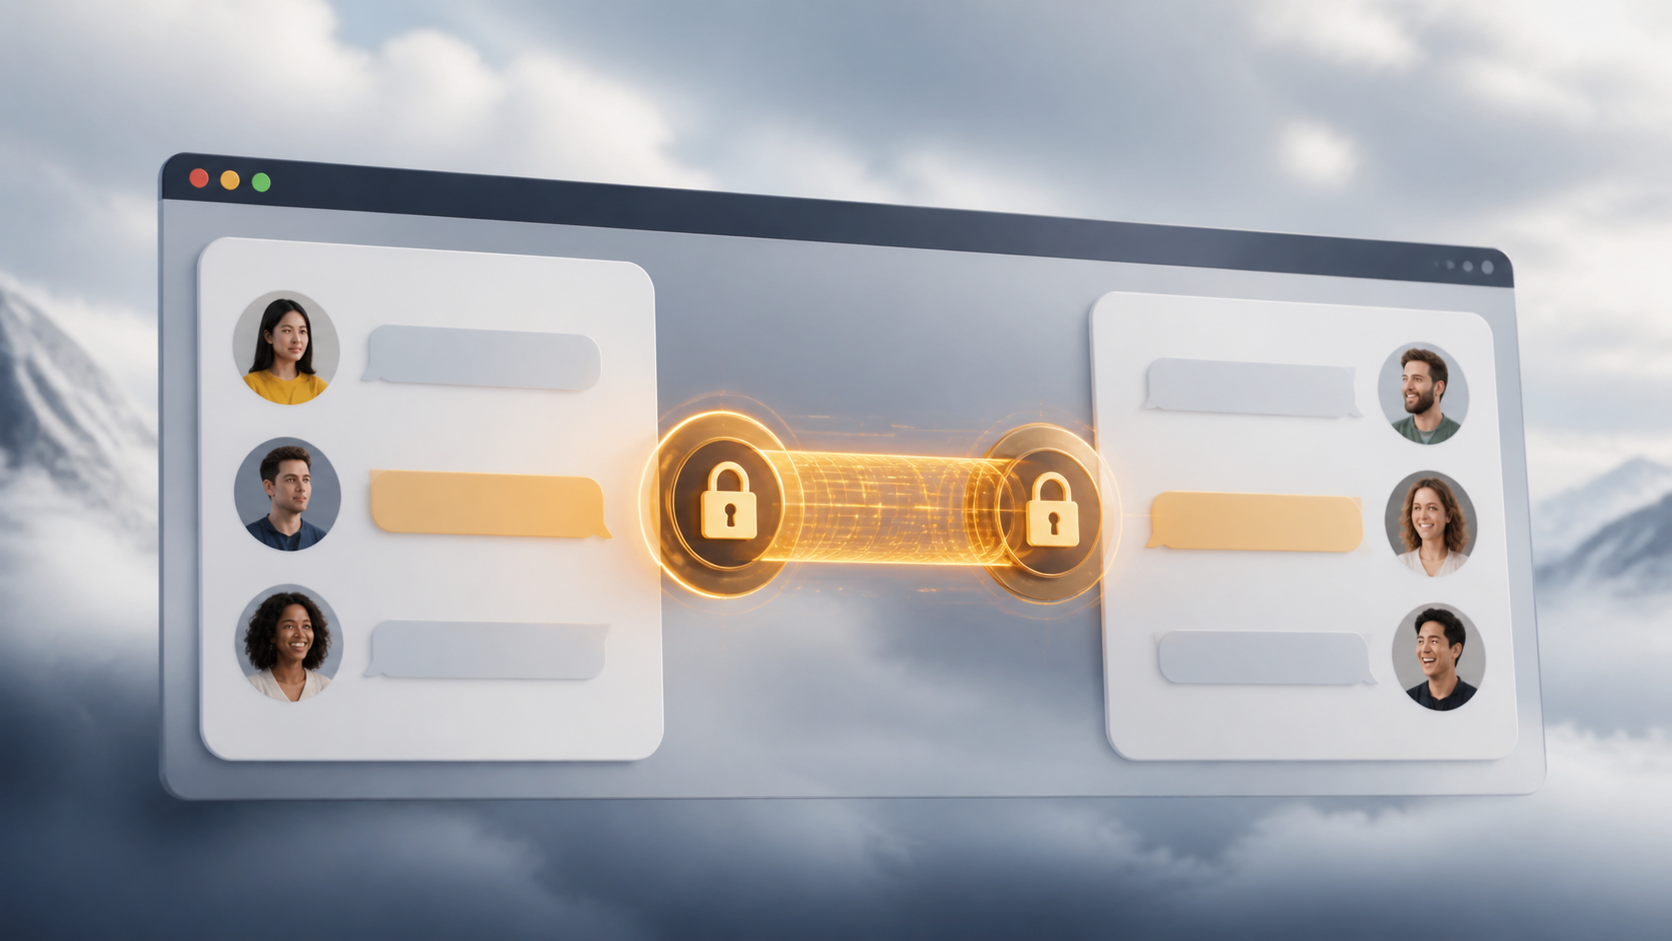
How end to end encryption chat works in browser
Understand how an end to end encryption chat app can work in a browser, what it protects, and what users should still look for before trusting it.
Browser-based encrypted chat can sound like a contradiction at first. If messages are typed into a web page, people naturally wonder who can see them, where they are stored, and whether the browser itself creates a weak point. The good news is that end to end encryption chat can work very well in a browser when the system is built so that only the people in the conversation can read the content.
The key idea is simple: messages are encrypted on your device before they leave it, and only decrypted on the recipient’s device. The server in the middle can help move data around, but it should not be able to read the message body. That is the basic promise behind encrypted private chats, whether they live in an app or in browser messaging.
In practice, the security comes from design choices, not from the fact that the chat happens in a browser. A privacy first chat app can be browser-based and still keep content private end to end if it handles keys, sessions, and delivery carefully. That is the model PigeonChat follows.
What end to end encryption means in a browser
End to end encryption means the sender’s browser turns plain text into ciphertext before it leaves the device. The recipient’s browser then reverses that process with the correct key. Anyone who intercepts the traffic, including the service operator, sees only unreadable data.
In a well-designed end to end encryption chat, the browser is not a special risk by default. It is just the place where the encryption and decryption happen. What matters is which keys are used, where they are stored, and whether the service ever receives those keys in a readable form.
This is why browser messaging can be secure without asking users to install a desktop client. The browser can generate keys locally, protect them in the session, and perform cryptographic operations on the device. The web server simply helps with account login, message routing, and syncing encrypted blobs.
How the message flow works
At a high level, the flow is straightforward. You write a message, your browser encrypts it, and the encrypted packet is sent to the service. The service forwards it to the recipient, who decrypts it locally. If stored for later delivery, the message should remain encrypted the whole time.
That means the backend never needs to understand the text. In a privacy first chat app, the server may know that a message exists, who it is for, and when it was delivered, but it should not know the message content. This is the difference between transport security and true end to end protection.
Here is the basic sequence:
- Your browser creates or loads cryptographic keys.
- A message is encrypted locally before it leaves the page.
- The server stores or relays only encrypted data.
- The recipient’s browser decrypts the message after it arrives.
- If you send attachments, they should follow the same rule.
That flow is what makes encrypted private chats genuinely private. A service such as the PigeonChat e2e chat app pigeonchat.site can be browser-based while still keeping the important part out of the server’s reach.
Where security actually comes from
Most of the trust in browser-based encrypted chat comes from key management. If keys are created locally and never exposed to the server, the operator cannot decrypt message content even if they wanted to. The same is true if the server is compromised, because encrypted content alone is not enough to read the chat.
Session security also matters. Good systems use strong, short-lived session handling so that authentication is convenient without exposing raw message keys unnecessarily. A secure browser messaging product should separate login credentials from the keys that protect conversation content.
Another important point is code integrity. Because browser chat runs in delivered web code, the service must be careful about how updates are deployed. A strong product will treat client code as part of the trust model and try to reduce the risk of silent changes that could weaken privacy. That is one reason people should prefer services that are explicit about their security approach.
Common concerns about browser messaging
People often ask whether browser-based encryption is weaker because browsers are connected to so much other software. The honest answer is that the browser does introduce a larger general attack surface than a single-purpose device, but that does not make secure chat impossible. It means the product has to be built with discipline.
Another concern is whether the server can change the code that runs in the browser. That is a fair question. A trustworthy browser messaging system should minimise this risk through careful deployment practices, integrity checks, and a design that does not depend on server-side access to readable content.
There is also the issue of metadata. End to end encryption protects message content, but not always everything around it. Depending on the product, the server may still know timing, device details, or routing information. A good privacy first chat app should be clear about what it can and cannot hide.
What to look for in a privacy first chat app
If you are evaluating an encrypted chat service, focus on the practical safeguards rather than buzzwords. The strongest claims are the ones that are specific about how keys are handled and what the server cannot see. A clear product description is usually more useful than vague promises of “military grade” privacy.
Useful signs include local encryption, minimal data collection, and a clear explanation of message storage. If a service says it offers encrypted private chats, it should also explain whether content is encrypted before upload, whether it can read messages, and how message history is protected.
It helps to ask a few direct questions:
- Are messages encrypted in the browser before they reach the server?
- Does the service ever have access to readable message content?
- How are keys created, stored, and refreshed?
- What metadata is kept, and for how long?
- Can the service support browser messaging without a separate app?
Services like PigeonChat are useful because they show that secure chat does not have to be tied to a native install. If the design is careful, the browser can be a perfectly sensible place for private conversations.
Why this model works for everyday use
For many people, the biggest advantage is convenience without giving up privacy. You can open a browser, log in, and start a protected conversation without asking the other person to download anything special. That lowers friction while keeping the content private end to end.
Browser-based encrypted chat is also easier to adopt across different devices. If your phone, work laptop, and home computer all support the same web app, the experience is more consistent. The important thing is that the privacy guarantees should remain the same on each device.
When the product is designed properly, encrypted private chats in the browser are not a compromise. They are a practical way to combine accessibility with strong confidentiality, as long as the service keeps its promise not to learn the message content.
Frequently asked questions
Is browser-based end to end encryption as safe as a native app?
It can be, provided the browser app is designed carefully. The main difference is not the browser itself, but how keys are handled, how code is delivered, and how much trust you place in the service’s implementation. A well-built browser messaging system can protect message content very effectively.
Can the server read my messages if the chat is truly end to end encrypted?
No, not if the system is implemented properly. The server may still route messages, store encrypted payloads, and manage account data, but it should not be able to decrypt the conversation content. If it can read messages, then it is not true end to end encryption.
What is the biggest risk with encrypted private chats in a browser?
The biggest risk is usually implementation quality, not the browser concept itself. Weak key handling, poor session design, or careless code updates can weaken privacy. That is why it matters to choose a privacy first chat app that explains its approach clearly and keeps the architecture simple.
In the end, how end to end encryption chat works in browser comes down to one principle: the server should help move data, not understand it. When that line is respected, browser messaging can support genuinely private conversations. That is the standard PigeonChat aims for, and the standard any serious encrypted private chats service should try to meet.
Ready to try PigeonChat?

Writer & Editor at PigeonChat
Related Articles

What makes an end to end encryption chat app secure

What a fully compliant EU chat app should include

Why people search for a WhatsApp alternative without a number

What end to end encryption chat really protects

Why chat folders matter for busy group conversations
